

 EN
 DE
Threeam Ransomware: What You Need to Know & How to Recover Fast
3AM talks its way past staff with spoofed IT help-desk calls and email bombing, then steals files before encrypting Windows systems with Conti-linked tooling. See how its RECOVER-FILES.txt notes work, why it kills backup software before encrypting, and — if your systems are compromised — how BeforeCrypt helps contain the attack and restore operations.
What is Threeam Ransomware?
3AM (ThreeAM) is a Russian-speaking, human-operated ransomware operation linked to the Conti/Royal/BlackSuit lineage, with trackers counting close to 100 leak-site victims since 2023 across manufacturing, professional services and healthcare in the US, UK, Germany and beyond, hitting everything from small firms to larger enterprises. Written in Rust for 64-bit Windows, it kills backup and security tools, deletes shadow copies, and exfiltrates data before encrypting it. Across 3AM engagements, BeforeCrypt helps contain the attack, assess recovery options and restore operations safely.

Rust-Based Windows Encryptor
3AM is a 64-bit Windows payload written in Rust, run with operator-set command-line parameters for each deployment.
Backup & Security Kill Chain
Before encrypting, it stops Veeam, Acronis, Ivanti, McAfee and Symantec services; after encryption it deletes Volume Shadow Copies.
Vishing & Quick Assist Access
Operators use email bombing and spoofed IT help-desk calls to talk staff into granting remote access via Quick Assist.
Double-Extortion Leak Site
Stolen data is exfiltrated before encryption and threatened with sale or publication on the group's Tor leak site.Why You Shouldn’t Attempt to Fix It Alone
Using an unverified tool on live data can make recovery harder, so any candidate should be tested on copies first. BeforeCrypt checks for available decryption tools, including free ones, as part of every assessment, and evaluates which recovery path actually fits your backups and systems.
3AM steals files before encrypting them, and its ransom note threatens to sell that data on the DarkNet if no deal is reached. Even where backups let you rebuild systems, the stolen data can still be published or sold — an additional risk for your business separate from the file loss itself. Notification obligations depend on your sector and geography — see the FAQ below for the regulatory clocks that may apply.
BeforeCrypt provides full incident response where a client has no internal capacity, or works alongside an existing IT team on forensic triage, containment and eradication. We establish what data was taken, screen for sanctions exposure before any payment, preserve evidence for insurers and regulators, and coordinate notification timelines. Where it’s the right option, our team handles negotiation with the attackers — including reducing the demand and buying time. Running technical response, internal coordination, and customer and regulator communication at the same time strains internal teams, especially with a double-extortion deadline running.
An experienced internal security team can handle substantial parts of the response itself. Our detailed emergency response plan walks through the sequence step by step. A free assessment call with our team helps you decide quickly which parts to keep in-house and where specialist support saves time.
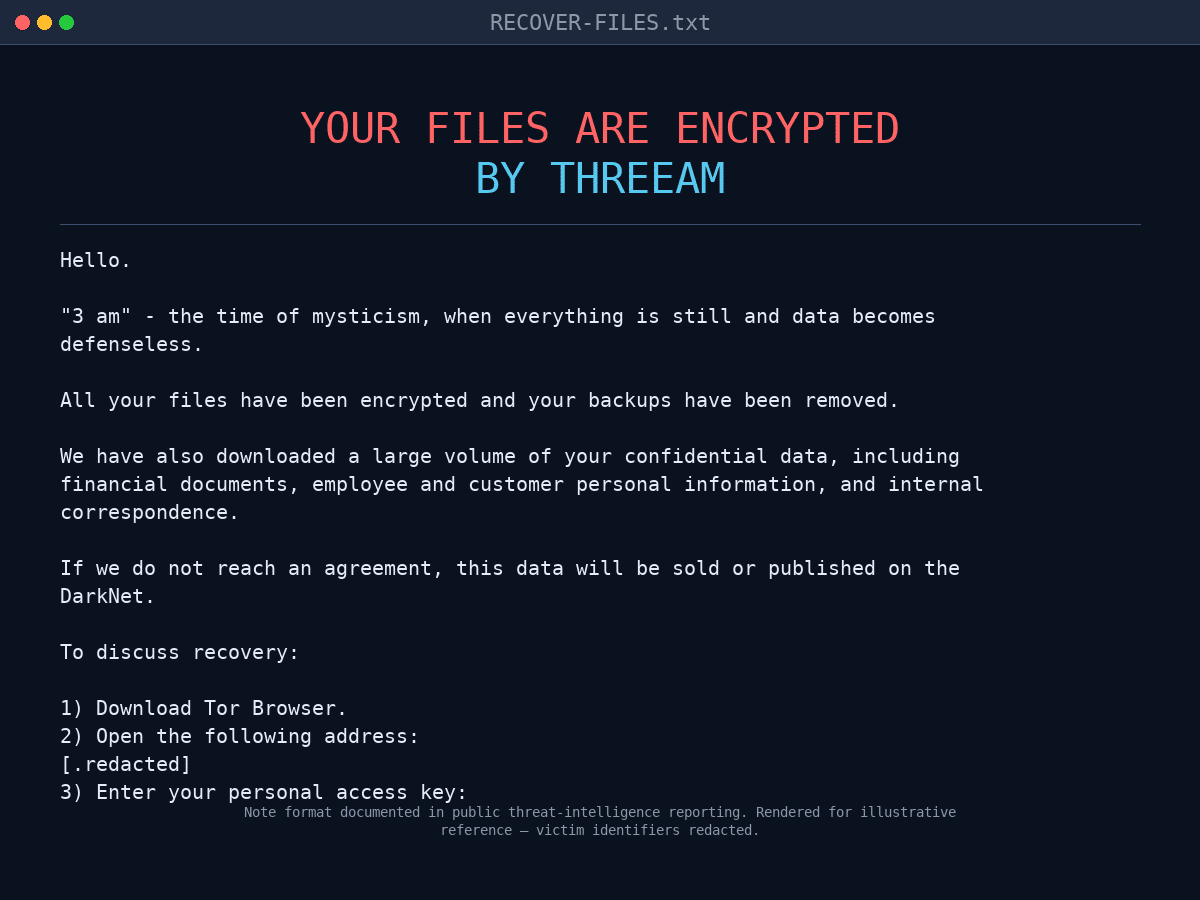
3AM drops a ransom note named RECOVER-FILES.txt into every folder it encrypts, opening with a reference to ‘3 am’ before describing stolen financial, employee and customer data. The note includes a 32-character access key tied to the encryptor’s -k parameter, which victims enter on the group’s Tor negotiation portal.
YOU MUST NOT ATTEMPT TO TOUCH, RESTORE OR OVERWRITE THE DATA.
Hit by Threeam Ransomware? Take These Immediate Recovery Steps
If you’ve fallen victim to ransomware, follow these crucial steps:
Request 24/7 Ransomware Recovery Help
Get expert guidance to assess, contain, and recover safely.
Isolate Infected Systems
Disconnect infected devices to stop the spread. Avoid self-recovery.
Preserve Evidence Immediately
Keep ransom notes & logs. Do not restart or modify anything.
Threeam ransomware statistics & facts
RANSOM SUMMARY
| Name | 3AM / ThreeAM |
| Danger level | High. Human-operated ransomware that steals data before encrypting Windows systems and deletes shadow copies to block recovery. |
| Release date | 2023 (first publicly documented September 2023) |
| OS affected | Windows (64-bit) |
| Appended file extensions | .threeamtime |
| Ransom note filename | RECOVER-FILES.txt |
| Contact channels | Tor negotiation portal, reached using a 32-character access key printed in the ransom note |
COMMON ATTACK VECTORS
- Spearphishing Voice (T1566.004) — email bombing combined with spoofed IT help-desk calls to trick staff into granting remote access.
- External Remote Services (T1133) — abuses Microsoft Quick Assist sessions granted by deceived employees for initial foothold.
- Valid Accounts (T1078) — compromises a domain administrator account for lateral movement and privilege escalation.
- Service Stop (T1489) — disables Veeam, Acronis, Ivanti, McAfee and Symantec services before encrypting.
- Inhibit System Recovery (T1490) — deletes Volume Shadow Copies after encryption to block restoration.
RANSOM AMOUNTS
3AM has hit small and mid-sized businesses across manufacturing, professional services and healthcare in the US, UK and Germany, in intrusions documented since 2025 gaining entry through vished IT help-desk calls that led staff to grant remote access via Microsoft Quick Assist.
Ransoms are usually paid in Bitcoin. Quick-buy methods of purchasing Bitcoin with PayPal or credit cards do not work for this size of ransom payment and it is important to obtain expert advice to ensure that a payment of this size is legally compliant.
Where negotiation is the right option, our experienced negotiation team has consistently secured meaningful reductions from the initial demand to the final settlement across Threeam engagements.
AVERAGE LENGTH
3AM disables backup software such as Veeam and Acronis before encrypting and deletes Volume Shadow Copies once encryption completes, and in a Q1 2025 case handled by Sophos Incident Response the actors remained in the network for nine days before deploying the encryptor, leaving teams to rebuild recovery options from scratch.
For most ransomware victims, downtime is the most costly aspect of the incident, with potential for considerable reputational harm.
Our extensive experience with Threeam ransomware gives us a deep understanding of the gang’s tactics, enabling us to resolve attacks swiftly and restore your files.
How to identify threeam ransomware
3AM drops RECOVER-FILES.txt in every folder it encrypts, opening with a reference to ‘3 am’ before listing the categories of stolen data and a Tor link with a 32-character access key tied to the encryptor’s -k parameter.
Frequently asked questions
Decryption depends on the ransomware variant. In some cases, publicly available decryption tools exist, but not all attacks have a known solution. You can submit a free ransomware recovery request, and we will check for possible decryption methods.
In most cases involving personal data, which applies to nearly every ransomware incident, reporting is legally required. In the EU, GDPR requires notification to the relevant data protection authority within 72 hours of becoming aware of a personal data breach. The UK ICO requires the same 72-hour window. In the US, HIPAA-covered entities have 60 days to notify affected individuals (and immediately for breaches affecting 500+ people). The clock starts from awareness of the incident, not from a full technical understanding.
In most jurisdictions, paying a ransom is not illegal in itself — but it can become illegal if the payment ends up going to a sanctioned entity or country (OFAC-designated groups in the US, EU sanctions lists, UK Treasury lists). Before any payment, sanctions screening is essential. BeforeCrypt handles this compliance layer as a standard part of every engagement.
Most established ransomware groups do provide working decryption tools when paid — the business model depends on their reputation for delivery. However, decryptors are often slow, incomplete, or corrupt a percentage of files during recovery. This is where working with a specialist matters: BeforeCrypt tracks the delivery reliability of specific groups, negotiates sample-file decryption as proof of capability where the group allows it, and plans realistic recovery timelines based on our own engagement history with each group.
Most modern ransomware groups follow through on publication threats — stolen data appears on the group's leak site, is often mirrored to Telegram and dark web forums, and may be sold to third parties. Recovery becomes limited to whatever you can rebuild from backups.
Backups protect against file loss but not against data theft. Most modern ransomware groups exfiltrate sensitive data BEFORE encryption and threaten to publish it regardless of your recovery capability. This is why leak-site publication and negotiation still matter even for organisations with clean, offline backups — and why "we can just restore from backup" rarely tells the full story.
In most jurisdictions, yes — reporting is a standard part of a ransomware incident and, in some cases, legally required. In the US, that means the FBI (via IC3 or a local field office) and CISA. In the EU, national CERT and cybercrime units. Reporting does not obligate you to any specific recovery path but does open access to threat intelligence and, occasionally, decryption tools recovered by law enforcement.
Yes. We’ve handled 1,700+ incidents across ransomware, BEC and data-leak extortion. We identify the variant, decide decrypt vs. clean verified restore, and guide a controlled return to operations. When needed, we support negotiation & compliance—always legally and with a clear audit trail.
Yes. We produce insurer-ready incident reports with a defensible timeline, scope, likely entry path, exfiltration assessment, actions taken, and chain-of-custody. We can join the adjuster call, map our findings to your carrier’s forms, and provide GDPR/NIS2 notifications where required. Final acceptance always depends on the policy and carrier, but our packages are designed to speed up approvals and reduce back-and-forth.
MSPs keep IT running; they’re not built for evidence handling and incident triage. Insurer panels optimize claims, not necessarily speed & clarity for your business. We work alongside both: kick off in ≤2h, run forensic triage with chain-of-custody, coordinate safe containment, and deliver executive- and insurer-ready findings—without taking your environment hostage.
Because it turns chaos into fast, safe recovery. We cut downtime and limit damage while preserving evidence. Within ≤48h you get a forensic triage pack (timeline, likely entry path, scope, decrypt-vs-clean-restore decision, go-live criteria) so leadership can act with confidence. Result: controlled, verified restart—not guesswork.