

 EN
 DE
N0n Ransomware: What You Need to Know & How to Recover Fast
N0n surfaced in September 2026, posting rapid bursts of victim claims across nine countries on its Tor leak site, with no ransom amount shown in the listings reviewed by third parties. See how its short UTC deadlines and private negotiation room pressure victims, why some listings may be fabricated, and how BeforeCrypt helps you verify and respond.
What is N0n Ransomware?
N0n is a Tor-based extortion operation that surfaced in September 2026, with public leak-site tracking counting 12 victim postings across nine countries that month alone, concentrated in financial services, retail and education. Researchers disagree on whether N0n actually encrypts systems or relies purely on the threat of publishing stolen data, and its listings have included claims flagged as unverified or fabricated. BeforeCrypt draws on experience across data-extortion incidents to help you confirm what N0n is actually claiming, contain the exposure and restore normal operations.

Tor Data-Leak Site
N0n runs a Tor-hosted leak site that posts victim claims with short, precise UTC deadlines.
No Stated Ransom Figure
Reviewed listings do not display a ransom amount; contact happens through a private negotiation room.
Cross-Sector Targeting
Listings span at least nine countries and sectors including financial services, retail, education and government.
Unverified Victim Claims
Independent reviewers have flagged some N0n postings as lacking proof or including fabricated victims.Why You Shouldn’t Attempt to Fix It Alone
Researchers disagree on whether N0n actually encrypts files or limits itself to threatening publication of stolen data, so the right recovery path depends on what happened on your systems. BeforeCrypt checks for available decryption tools, including free ones, as part of every assessment, and any tool is tested on copies first because an unverified or unsuitable one can make recovery harder rather than easier. Where no encryption occurred, recovery focuses on containment and confirming what data left your network.
N0n’s leak-site listings describe stolen data — network maps, client documents, investor and order records — and threaten to publish it in batches once a short deadline passes, regardless of whether encryption is involved. Even organisations that restore from backups still face this additional risk of public disclosure or sale of what was taken. Notification obligations depend on your sector and geography — see the FAQ below for the regulatory clocks that may apply.
Because N0n’s own postings can’t be taken at face value — reviewers found no proof artefacts, and some claims resemble fabricated victims — BeforeCrypt helps confirm what was actually taken, working alongside your IT team or leading the response where needed. N0n has added regulatory pressure in at least one case by threatening to send investor data to tax authorities; where negotiation is the right route, BeforeCrypt handles attacker contact, including reducing the demand and buying time, alongside sanctions screening and evidence preservation. Coordinating technical response, internal teams, customer communication and any attacker contact at once is a lot to carry simultaneously.
An experienced internal security team can handle substantial parts of the response itself. Our detailed emergency response plan walks through the sequence step by step. A free assessment call with our team helps you decide quickly which parts to keep in-house and where specialist support saves time.
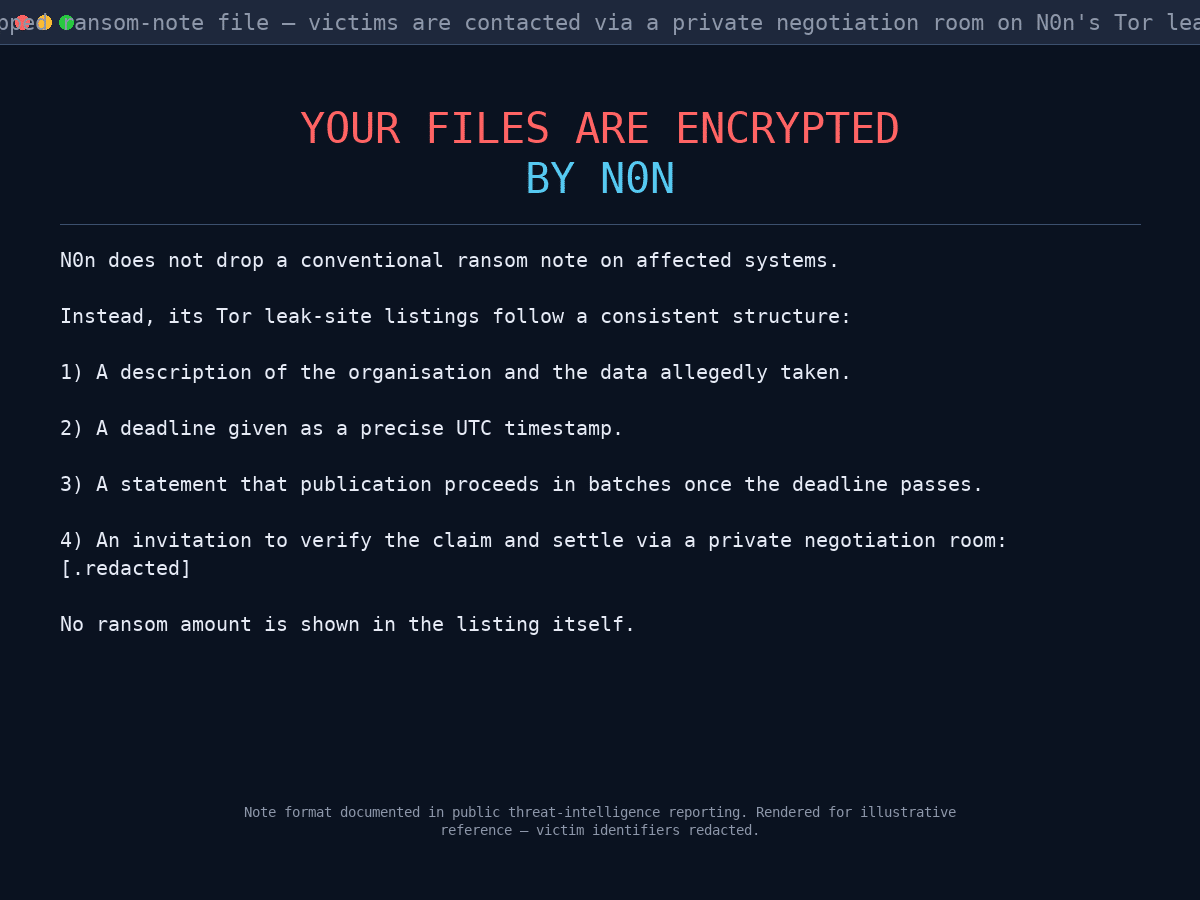
N0n does not appear to drop a traditional ransom-note file on affected systems; instead, each Tor leak-site listing carries a precise UTC deadline and an invitation to verify the claimed data and settle. There is no fixed ransom figure in the listing itself — amounts, if any, are only discussed once a victim enters the group’s private negotiation room.
YOU MUST NOT ATTEMPT TO TOUCH, RESTORE OR OVERWRITE THE DATA.
Hit by N0n Ransomware? Take These Immediate Recovery Steps
If you’ve fallen victim to ransomware, follow these crucial steps:
Request 24/7 Ransomware Recovery Help
Get expert guidance to assess, contain, and recover safely.
Isolate Infected Systems
Disconnect infected devices to stop the spread. Avoid self-recovery.
Preserve Evidence Immediately
Keep ransom notes & logs. Do not restart or modify anything.
N0n ransomware statistics & facts
RANSOM SUMMARY
| Name | N0n |
| Danger level | Disputed. Published threat-intelligence profiles assess N0n as data-extortion without encryption; WatchGuard classifies it as double extortion — treat leak-site claims as unverified until corroborated. |
| Release date | 2026 (first observed September 2026) |
| Ransom note filename | No dropped ransom-note file has surfaced; contact occurs through a private negotiation room linked from the group’s Tor leak-site listings |
| Contact channels | Tor-hosted data-leak site with a private negotiation room |
COMMON ATTACK VECTORS
In September 2026, reviewers found that no initial-access technique, exploited vulnerability or MITRE ATT&CK mapping had been disclosed for N0n in any vendor or government source examined. In September 2026, published threat-intelligence profiles recorded no tooling and no observed techniques for the group. Treat any specific claim about how N0n gains access with caution until further analysis is published.
RANSOM AMOUNTS
N0n’s leak-site listings span financial services, retail and education organisations across at least nine countries, with the United States and Vietnam appearing most often in its September 2026 postings.
N0n’s leak-site listings do not display a ransom figure; amounts are only discussed once a victim enters the group’s private negotiation room. Where a demand is made, ransoms of this kind are usually paid in Bitcoin. Quick-buy methods of purchasing Bitcoin with PayPal or credit cards do not work for this size of payment, and it is important to obtain expert advice to ensure any payment is legally compliant.
Where negotiation is the right option, our experienced negotiation team has consistently secured meaningful reductions from the initial demand to the final settlement across N0n engagements.
AVERAGE LENGTH
N0n’s own listings claim that backups and shadow copies have been encrypted or destroyed and that operations are fully stopped, though these are unverified assertions from the group itself; confirming what actually happened is often the first step before any recovery timeline can be set.
For most ransomware victims, downtime is the most costly aspect of the incident, with potential for considerable reputational harm.
Our extensive experience with N0n ransomware gives us a deep understanding of the gang’s tactics, enabling us to resolve attacks swiftly and restore your files.
How to identify n0n ransomware
N0n does not appear to drop a traditional ransom-note file on affected systems; instead, each Tor leak-site listing carries a precise UTC deadline, a description of the data claimed to be stolen, and an invitation to verify and settle in a private negotiation room.
Frequently asked questions
Decryption depends on the ransomware variant. In some cases, publicly available decryption tools exist, but not all attacks have a known solution. You can submit a free ransomware recovery request, and we will check for possible decryption methods.
In most cases involving personal data, which applies to nearly every ransomware incident, reporting is legally required. In the EU, GDPR requires notification to the relevant data protection authority within 72 hours of becoming aware of a personal data breach. The UK ICO requires the same 72-hour window. In the US, HIPAA-covered entities have 60 days to notify affected individuals (and immediately for breaches affecting 500+ people). The clock starts from awareness of the incident, not from a full technical understanding.
In most jurisdictions, paying a ransom is not illegal in itself — but it can become illegal if the payment ends up going to a sanctioned entity or country (OFAC-designated groups in the US, EU sanctions lists, UK Treasury lists). Before any payment, sanctions screening is essential. BeforeCrypt handles this compliance layer as a standard part of every engagement.
Most established ransomware groups do provide working decryption tools when paid — the business model depends on their reputation for delivery. However, decryptors are often slow, incomplete, or corrupt a percentage of files during recovery. This is where working with a specialist matters: BeforeCrypt tracks the delivery reliability of specific groups, negotiates sample-file decryption as proof of capability where the group allows it, and plans realistic recovery timelines based on our own engagement history with each group.
Most modern ransomware groups follow through on publication threats — stolen data appears on the group's leak site, is often mirrored to Telegram and dark web forums, and may be sold to third parties. Recovery becomes limited to whatever you can rebuild from backups.
Backups protect against file loss but not against data theft. Most modern ransomware groups exfiltrate sensitive data BEFORE encryption and threaten to publish it regardless of your recovery capability. This is why leak-site publication and negotiation still matter even for organisations with clean, offline backups — and why "we can just restore from backup" rarely tells the full story.
In most jurisdictions, yes — reporting is a standard part of a ransomware incident and, in some cases, legally required. In the US, that means the FBI (via IC3 or a local field office) and CISA. In the EU, national CERT and cybercrime units. Reporting does not obligate you to any specific recovery path but does open access to threat intelligence and, occasionally, decryption tools recovered by law enforcement.
Yes. We’ve handled 1,700+ incidents across ransomware, BEC and data-leak extortion. We identify the variant, decide decrypt vs. clean verified restore, and guide a controlled return to operations. When needed, we support negotiation & compliance—always legally and with a clear audit trail.
Yes. We produce insurer-ready incident reports with a defensible timeline, scope, likely entry path, exfiltration assessment, actions taken, and chain-of-custody. We can join the adjuster call, map our findings to your carrier’s forms, and provide GDPR/NIS2 notifications where required. Final acceptance always depends on the policy and carrier, but our packages are designed to speed up approvals and reduce back-and-forth.
MSPs keep IT running; they’re not built for evidence handling and incident triage. Insurer panels optimize claims, not necessarily speed & clarity for your business. We work alongside both: kick off in ≤2h, run forensic triage with chain-of-custody, coordinate safe containment, and deliver executive- and insurer-ready findings—without taking your environment hostage.
Because it turns chaos into fast, safe recovery. We cut downtime and limit damage while preserving evidence. Within ≤48h you get a forensic triage pack (timeline, likely entry path, scope, decrypt-vs-clean-restore decision, go-live criteria) so leadership can act with confidence. Result: controlled, verified restart—not guesswork.