

 EN
 DE
Thegentlemen Ransomware: What You Need to Know & How to Recover Fast
The Gentlemen’s affiliates enter through stolen Fortinet VPN credentials, then encrypt Windows, Linux, ESXi and NAS systems within days across manufacturing, healthcare and professional-services firms worldwide. See how its ransom notes threaten to publish stolen data, what its self-spreading encryptor does inside a network, and — if your systems are compromised — how BeforeCrypt’s team contains the attack and helps restore operations.
What is Thegentlemen Ransomware?
The Gentlemen is a ransomware-as-a-service operation that emerged in mid-2025 and was linked to hundreds of published victims across manufacturing, healthcare and professional-services firms by mid-2026, according to published vendor research. Its Go- and C-based lockers reach Windows, Linux, ESXi, NAS and BSD systems, combining per-file Curve25519 key exchange with XChaCha20 encryption and a module that spreads itself across a network before locking files. BeforeCrypt’s experience across Gentlemen engagements helps contain the attack, evaluate recovery options and restore operations safely.

Self-Propagating Encryptor
An automated module fires multiple lateral-movement techniques at once to spread across a network before encryption begins.
Cross-Platform Targeting
Separate Go- and C-based builds let affiliates encrypt Windows, Linux, ESXi, NAS and BSD systems in the same intrusion.
Custom EDR-Killer Toolkit
Operators supply affiliates with an in-house EDR-killing framework that disables security products before encryption runs.
Double-Extortion Leak Site
Stolen data is posted to a Tor leak site with a countdown deadline if the ransom goes unpaid.Why You Shouldn’t Attempt to Fix It Alone
BeforeCrypt checks for available decryption tools, including free ones, as part of every assessment of a Gentlemen incident. The encryptor’s partial-encryption mode can leave large sections of bigger files unencrypted, which sometimes allows format-aware salvage of readable data — this is recovery, not decryption, and depends on the file types involved. An unverified tool applied to the wrong build can make recovery harder, so anything tested runs against copies of the affected files first.
The Gentlemen exfiltrates data before encrypting it, and even where backups bring files back cleanly, the stolen copies can still be published or sold through the group’s leak site. This is an additional risk for your business, separate from file recovery, since customer, employee or partner data may already be out of your control. Notification obligations depend on your sector and geography — see the FAQ below for the regulatory clocks that may apply.
BeforeCrypt runs full incident response where a client has no internal capacity, or works alongside an existing IT team on forensic triage, containment and eradication. This includes establishing what data was taken, screening any proposed payment against sanctions lists, preserving evidence for insurers and regulators, and — where it is the right route — negotiating with the attackers, including reducing the demand and buying time. Handling technical response, internal coordination, customer and regulator communication and any attacker contact at once strains internal teams, whatever their skill level.
An experienced internal security team can handle substantial parts of the response itself. Our detailed emergency response plan walks through the sequence step by step. A free assessment call with our team helps you decide quickly which parts to keep in-house and where specialist support saves time.
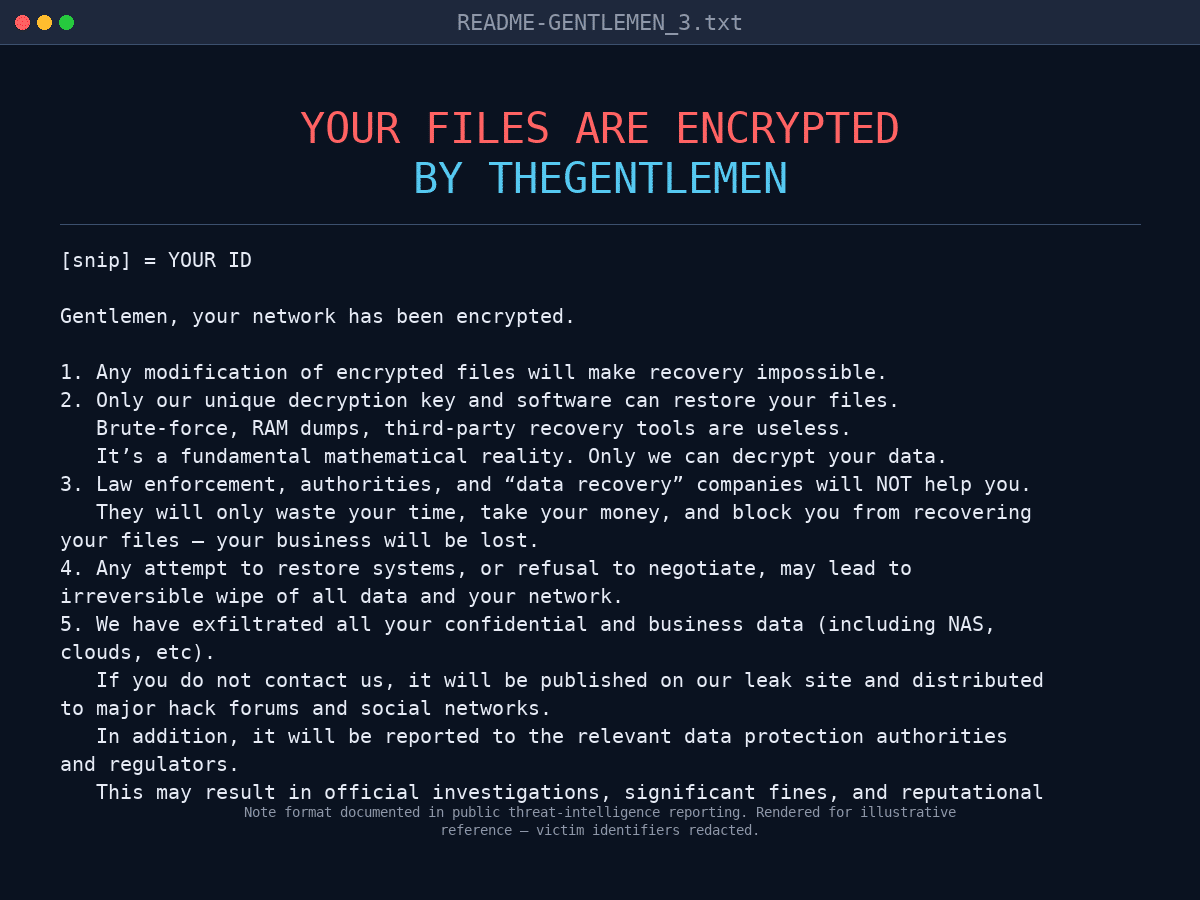
The note drops as README-GENTLEMEN.txt in every scanned folder, is excluded from encryption so it stays readable, and carries a victim-specific ID along with Tor portal and Tox contact details. Encrypted files themselves carry a random six-character extension that changes between builds, so the extension alone will not confirm the variant.
YOU MUST NOT ATTEMPT TO TOUCH, RESTORE OR OVERWRITE THE DATA.
Hit by Thegentlemen Ransomware? Take These Immediate Recovery Steps
If you’ve fallen victim to ransomware, follow these crucial steps:
Request 24/7 Ransomware Recovery Help
Get expert guidance to assess, contain, and recover safely.
Isolate Infected Systems
Disconnect infected devices to stop the spread. Avoid self-recovery.
Preserve Evidence Immediately
Keep ransom notes & logs. Do not restart or modify anything.
The Gentlemen ransomware statistics & facts
RANSOM SUMMARY
| Name | The Gentlemen (tracked as Storm-2697, GOLD SHERWOOD, LARVA-368) |
| Danger level | Very High. Self-propagating, double-extortion ransomware that spreads automatically across a network before encrypting. |
| Release date | 2025 (first observed mid-2025) |
| OS affected | Windows, Linux, VMware ESXi, NAS/BSD |
| Appended file extensions | Random six-character extension that varies per build (e.g. .7mtzhh, .umc16h) |
| Ransom note filename | README-GENTLEMEN.txt |
| Contact channels | Tor-based contact portal with victim-specific ID; Tox ID |
COMMON ATTACK VECTORS
Documented MITRE ATT&CK initial-access and execution techniques used by The Gentlemen.
- Valid Accounts (T1078) — affiliates use stolen Fortinet SSL-VPN credentials, reportedly supplied by the group’s administrator from a stockpiled credential database.
- External Remote Services (T1133) — compromised VPN access and exposed management interfaces on edge devices provide the initial foothold.
- Impair Defenses (T1562) — a custom in-house EDR-killer framework and signed vulnerable drivers disable endpoint protection before encryption runs.
- Lateral Tool Transfer / Remote Services (T1570 / T1021) — an automated module fires PsExec, WMI, scheduled tasks and PowerShell remoting simultaneously to spread across hosts.
- Exfiltration to Cloud Storage (T1567) — Rclone, MEGAsync and similar tools stage stolen data before the encryptor runs.
RANSOM AMOUNTS
The Gentlemen’s affiliates typically target manufacturing, professional-services and healthcare organisations of varying sizes, gaining entry through compromised Fortinet VPN credentials and exposed edge devices.
In one negotiation transcript analysed in published threat-intelligence research, an opening demand of about $250,000 was settled at roughly $190,000; leaked internal material shows demands calibrated to victim finances, in one documented case set to match a victim’s $10 million cyber insurance ceiling. Ransoms are usually paid in Bitcoin. Quick-buy methods of purchasing Bitcoin with PayPal or credit cards do not work for this size of ransom payment and it is important to obtain expert advice to ensure that a payment of this size is legally compliant.
Where negotiation is the right option, our experienced negotiation team has consistently secured meaningful reductions from the initial demand to the final settlement across The Gentlemen engagements.
AVERAGE LENGTH
Across 15 intrusions analysed in published incident-response research, some of The Gentlemen’s affiliates deployed ransomware in under 24 hours from the first observed post-compromise activity, with a median time to deployment of roughly two days, deleting shadow copies, clearing event logs and disabling backup and security services along the way, leaving little time to prepare a response.
For most ransomware victims, downtime is the most costly aspect of the incident, with potential for considerable reputational harm.
Our extensive experience with The Gentlemen ransomware gives us a deep understanding of the gang’s tactics, enabling us to resolve attacks swiftly and restore your files.
How to identify thegentlemen ransomware
The note drops as README-GENTLEMEN.txt in every folder the encryptor scans and is excluded from encryption so it stays readable. It states that recovery without the attackers’ key is impossible, gives Tor portal and Tox contact details tied to a victim-specific ID, and warns that stolen data will be published if the ransom goes unpaid.
Frequently asked questions
Decryption depends on the ransomware variant. In some cases, publicly available decryption tools exist, but not all attacks have a known solution. You can submit a free ransomware recovery request, and we will check for possible decryption methods.
In most cases involving personal data, which applies to nearly every ransomware incident, reporting is legally required. In the EU, GDPR requires notification to the relevant data protection authority within 72 hours of becoming aware of a personal data breach. The UK ICO requires the same 72-hour window. In the US, HIPAA-covered entities have 60 days to notify affected individuals (and immediately for breaches affecting 500+ people). The clock starts from awareness of the incident, not from a full technical understanding.
In most jurisdictions, paying a ransom is not illegal in itself — but it can become illegal if the payment ends up going to a sanctioned entity or country (OFAC-designated groups in the US, EU sanctions lists, UK Treasury lists). Before any payment, sanctions screening is essential. BeforeCrypt handles this compliance layer as a standard part of every engagement.
Most established ransomware groups do provide working decryption tools when paid — the business model depends on their reputation for delivery. However, decryptors are often slow, incomplete, or corrupt a percentage of files during recovery. This is where working with a specialist matters: BeforeCrypt tracks the delivery reliability of specific groups, negotiates sample-file decryption as proof of capability where the group allows it, and plans realistic recovery timelines based on our own engagement history with each group.
Most modern ransomware groups follow through on publication threats — stolen data appears on the group's leak site, is often mirrored to Telegram and dark web forums, and may be sold to third parties. Recovery becomes limited to whatever you can rebuild from backups.
Backups protect against file loss but not against data theft. Most modern ransomware groups exfiltrate sensitive data BEFORE encryption and threaten to publish it regardless of your recovery capability. This is why leak-site publication and negotiation still matter even for organisations with clean, offline backups — and why "we can just restore from backup" rarely tells the full story.
In most jurisdictions, yes — reporting is a standard part of a ransomware incident and, in some cases, legally required. In the US, that means the FBI (via IC3 or a local field office) and CISA. In the EU, national CERT and cybercrime units. Reporting does not obligate you to any specific recovery path but does open access to threat intelligence and, occasionally, decryption tools recovered by law enforcement.
Yes. We’ve handled 1,700+ incidents across ransomware, BEC and data-leak extortion. We identify the variant, decide decrypt vs. clean verified restore, and guide a controlled return to operations. When needed, we support negotiation & compliance—always legally and with a clear audit trail.
Yes. We produce insurer-ready incident reports with a defensible timeline, scope, likely entry path, exfiltration assessment, actions taken, and chain-of-custody. We can join the adjuster call, map our findings to your carrier’s forms, and provide GDPR/NIS2 notifications where required. Final acceptance always depends on the policy and carrier, but our packages are designed to speed up approvals and reduce back-and-forth.
MSPs keep IT running; they’re not built for evidence handling and incident triage. Insurer panels optimize claims, not necessarily speed & clarity for your business. We work alongside both: kick off in ≤2h, run forensic triage with chain-of-custody, coordinate safe containment, and deliver executive- and insurer-ready findings—without taking your environment hostage.
Because it turns chaos into fast, safe recovery. We cut downtime and limit damage while preserving evidence. Within ≤48h you get a forensic triage pack (timeline, likely entry path, scope, decrypt-vs-clean-restore decision, go-live criteria) so leadership can act with confidence. Result: controlled, verified restart—not guesswork.